


Corporate Bureaucracy Is Slowing Your AI Initiative. Here Is Where It Hits Hardest

October 2, 2026
- 81% of financial services firms are adopting AI, yet traditional banks lag fintechs by a wide margin at every maturity stage.
- The gap is organizational structure. Approval chains, siloed data governance, and compliance processes weren't built for AI iteration cycles.
- Banks slow to adapt risk losing $170 billion in profit pools over the next decade.
- DBS reduced AI project timelines from 15 months to under 3 months by redesigning governance.
- Five structural changes fintech and banking leaders can apply now to reduce bureaucratic drag on AI rollouts.
The situation that may be familiar to many of us: your AI initiative is stalling because your internal processes were designed for a different era entirely.
A CTO in a regulated financial organization knows this feeling. The use case is approved, the vendor is selected, and the data exists. But the rollout keeps slipping. Sequential sign-off chains, compliance reviews, and data governance committees move at their own pace regardless of the business urgency you carry.
Corporate bureaucracy is the primary brake on AI adoption inside financial institutions today. This article maps where it hits hardest. It draws on what the original DashDevs analysis got right about the hybrid model. And it gives you a practical framework for cutting through.
What Is Corporate Bureaucracy?
It is the system of formal rules, hierarchical approval structures, and procedural requirements through which an organization makes and implements decisions.
Max Weber described it first in 1921 as a mechanism for accountability and consistency. And in that framing, bureaucracy has real advantages. It enables clear delegation, reduces favoritism, creates predictable decision paths, and makes organizations scalable and auditable. For regulated financial institutions, those advantages are not incidental. They are legally required in many cases.
The problem is that structures have not been redesigned for the iteration cycles that AI development requires. What worked for approving a new branch policy does not work for a machine learning model on a quarterly retraining cycle.
That gap is where most AI initiatives in banking get stuck.
The Advantages Worth Preserving
Before identifying what to remove, it is worth being precise about what to keep. The original DashDevs analysis was right to note that some degree of structured process is not optional for financial organizations.
Bureaucracy earns its place when:
- Maintaining compliance documentation: audit trails, model governance records, and data lineage are genuine requirements.
- Managing accountability: clear ownership of AI decisions, especially those affecting customers, is a regulatory expectation in most jurisdictions.
- Protecting sensitive data: data governance frameworks for financial institutions exist for legitimate reasons. The goal is to make them AI-compatible.
- Operating at scale: a bank running 370 AI models, as DBS does, needs governance infrastructure. The question is how that infrastructure is designed.
The target is bureaucracy calibrated to risk.
The Adoption Gap: What the Numbers Actually Show
According to the Cambridge Centre for Alternative Finance’s 2026 Global AI in Financial Services Report, based on 628 organizations across 151 jurisdictions, 81% of financial services firms are adopting AI at some level. That number sounds like momentum.
The detail underneath it doesn’t.
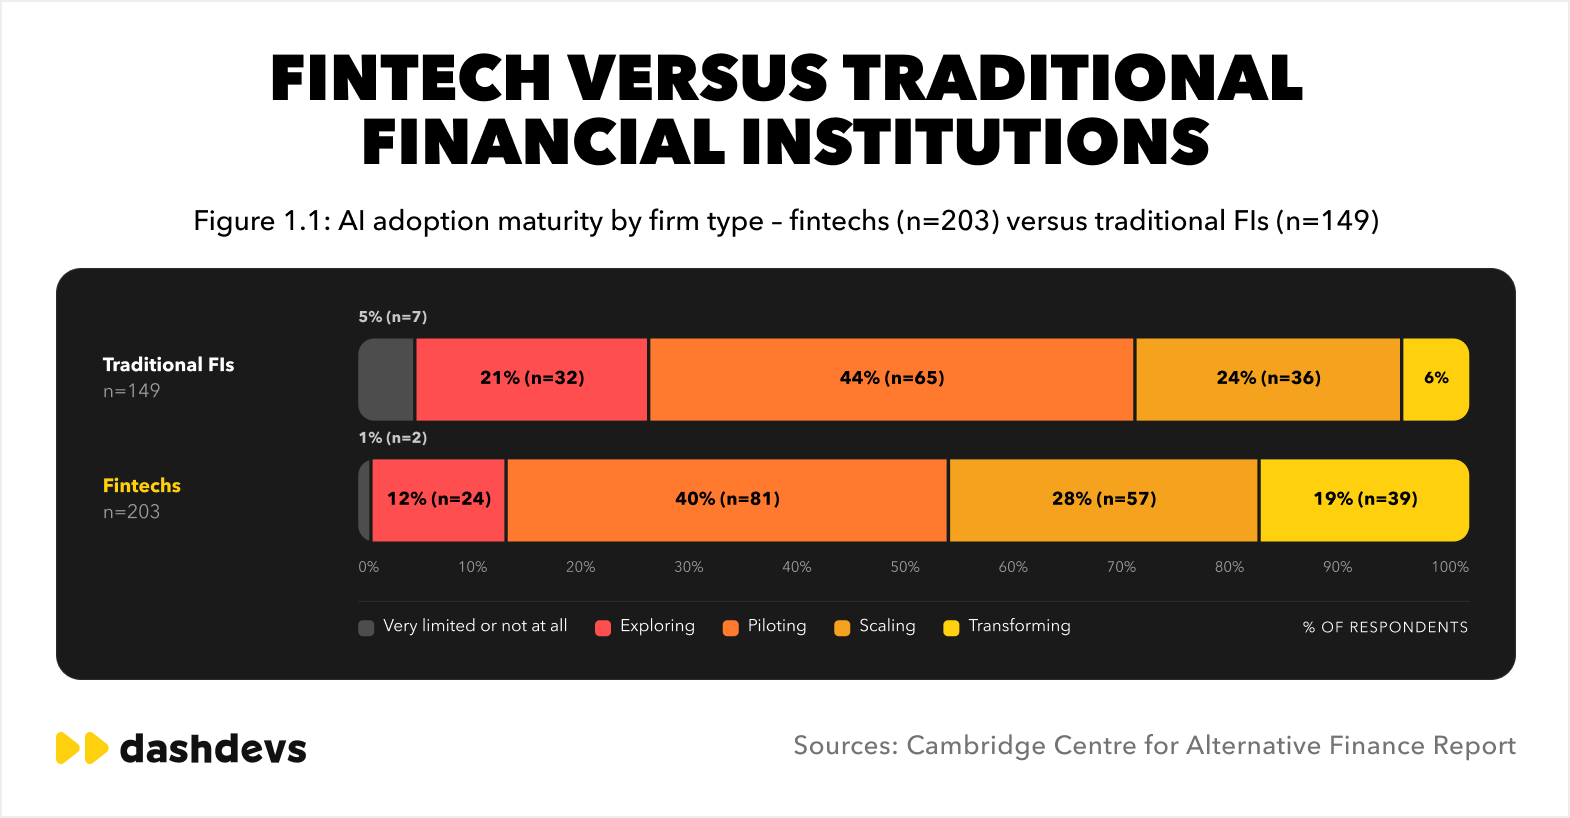
Fintechs lead traditional financial institutions at every stage of AI maturity:
- At the advanced adoption stage: fintechs 47%, incumbents 30%.
- At the transforming stage, where AI reshapes the business model: fintechs 19%, incumbents 6%.
- Incumbents show higher shares of Exploring (21%) and Piloting (44%), which is another way of saying they are stuck before production.
Both incumbents and fintechs access the same foundation models, the same cloud infrastructure, and increasingly the same vendor ecosystem. According to the same CCAF report, the disparity reflects that fintechs are digital-first and more agile, while traditional FIs face organizational inertia and legacy complexity.
The cost of staying in pilot mode is not abstract. McKinsey’s Global Banking Annual Review warns that banks that fail to reposition their business models risk losing $170 billion in global profit pools over the next decade, roughly 9% of projected 2030 banking profits.
Where Bureaucracy Hits AI Hardest in Financial Organizations
Siloed Data Governance Is the Leading Barrier
The CCAF report identifies data availability and quality as the leading barrier to AI adoption across financial services, cited by 49% of traditional financial institutions. AI vendors working with incumbent clients report the same. 46% flag legacy systems and siloed environments as a specific blocker. Another 41% cite data-sharing restrictions.
A fraud detection model needs transaction data, behavioral data, and identity data. In most large financial institutions, those datasets sit in separate systems. Each is owned by a different department. Each has its own access policies and approval chains. Getting cross-functional data access can take longer than building the model itself.
This is bureaucracy in business management operating as Weber described. Clear domain ownership, clear rules, and no cross-functional flexibility. The data governance framework was built to protect data assets within the organization. It wasn’t built to enable AI teams to move across those domains quickly.
DashDevs’ engineering teams encounter this regularly. Clients arrive with strong AI ambitions and a fintech architecture that requires six separate approvals before a data scientist can run a training job.
Sequential Approval Chains Were Not Built for Iteration
AI development is iterative. A model requires testing, retraining, threshold adjustment, and repeated evaluation before it is production-ready. Each iteration should be a short feedback loop. In most banks, it is not.
Most financial institutions run compliance review, data governance sign-off, vendor risk assessment, and legal review as a sequential chain. Each step waits for the previous one to complete. For a model that needs five iterations before it is ready, that chain runs five times.
The result is that what should be a 6-week improvement cycle becomes a 6-month approval sequence. These are the digital transformation challenges in banking that compound over time and explain why incumbents show 44% still at the piloting stage.
DBS Bank offers a direct contrast. The bank’s implementation of a centralized data platform and AI protocol repository reduced AI project timelines from 15 months to under 3 months. As of mid-2025, DBS has deployed over 1,500 AI models across 370 use cases. That output requires governance designed for volume, not governance that treats every deployment as a novel event.
Compliance Ambiguity Drives Conservative Defaults
Compliance teams inside banks aren’t slow because they want to obstruct AI. They are slow because the regulatory environment genuinely lacks clarity. The CCAF 2026 report found that 69% of industry respondents ranked clearer regulatory guidance as a top priority. When compliance teams face ambiguity, the rational default is caution. That means applying the same review intensity to a low-risk internal analytics tool as to a customer-facing credit decisioning model. That default isn’t irrational. But it is expensive. And it isn’t the same thing as a genuine compliance requirement.
Balancing fintech compliance and deployment speed is one of the DashDevs team’s work through every regulated product build.
The key question is always: is this approval step in the regulation, or did it accumulate around the regulation?
Legacy Architecture Makes Everything Slower
The CCAF 2026 report adds another dimension. Traditional FIs are far more reliant on on-premises or local cloud deployments (39%) than fintechs (23%). Legacy infrastructure is an AI velocity problem. Models that need to connect to on-premises data systems face integration complexity that cloud-native fintechs simply don’t have.
RPA in fintech has demonstrated this at scale. Automation at volume requires a data and integration architecture that most legacy bank systems weren’t built to support. The same constraint applies to AI at higher complexity.
AI vs. Bureaucracy: Where the Friction Points Are
The table below maps the most common bureaucratic friction points in financial institutions against what AI deployment actually requires. The mismatch column is where time and money disappear.
| Friction Point | What AI Requires | Consequence of Mismatch |
|---|---|---|
| Sequential approval cycles | Parallel, iterative review loops | Each iteration adds months to deployment |
| Siloed data governance | Cross-functional data access by default | Model quality limited by training data access |
| Uniform risk assessment | Risk-tiered governance by use case | Low-risk automation blocked at the same rate as high-risk decisions |
| On-premises data infrastructure | Cloud-accessible, API-ready data | Integration complexity slows every build |
| Compliance sign-off without AI expertise | Reviewers who understand model risk | Conservative defaults applied uniformly |
| IT-led AI ownership | Business unit ownership of AI outcomes | No commercial mandate to push through internal resistance |
The innovative fintech solutions that have moved from pilot to production at scale have one thing in common: they resolved the right-hand column before the model was built.
The Hybrid Model: What the Original Analysis Got Right
Financial organizations can’t choose between bureaucracy and no bureaucracy. They operate in a regulated environment. The real question is which processes are calibrated to actual risk and which ones are not.
Agentic AI payments reach production at fintechs while incumbents still discuss governance frameworks, precisely because fintechs built compliance into their architecture from the start rather than adding it as a sequential review layer afterward. The goal is compliance as infrastructure.
This is also the distinction DORA operational resilience controls for fintechs are increasingly formalizing: resilience and governance requirements that are designed around operating reality.
The speed at which AI capability is evolving is roughly 5x the speed at which governance and control frameworks are evolving. We need to close that gap before we allow autonomy.
That gap is the operational definition of excessive bureaucracy in the context of AI. The capability exists. The governance has not caught up. The organizations winning at AI are the ones actively closing that gap.
5 Ways to Reduce Bureaucratic Drag on AI Initiatives
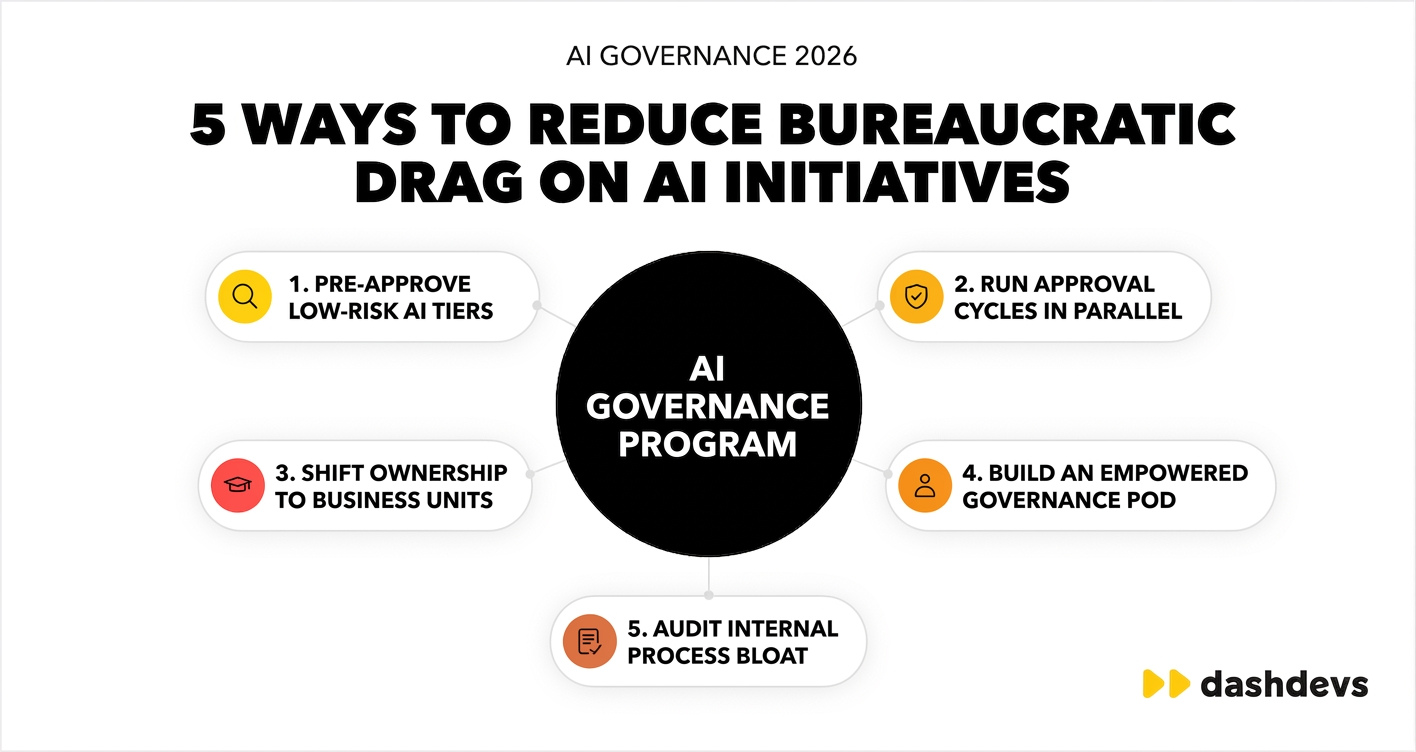
These five approaches reflect what is working in production across institutions in 2025-2026.
1. Map your AI use cases into risk tiers before any initiative arrives
Define in advance what a standard low-risk AI application looks like in your organization and pre-approve the governance template for that category. Initiatives that fit a pre-approved template move on an accelerated track. DBS reduced AI project timelines from 15 months to under 3 months this way. The mechanism was a centralized data platform combined with reusable model templates that avoided treating every deployment as a novel governance event. Our AI in banking use cases guide is a practical place to start that inventory.
2. Run approval cycles in parallel for low-risk applications
Most banks run compliance review, data governance sign-off, vendor risk assessment, and legal review as a sequential chain. For lower-risk use cases, there is no technical or regulatory reason these can’t happen simultaneously. The sequential structure is a process design choice. For AI use cases in banking that have been risk-tiered appropriately, parallel review can cut approval time by half without changing the rigor of any individual review.
3. Move AI initiative ownership from IT to business units
The CCAF 2026 report identifies organizational inertia as a key factor in the gap between fintechs and incumbents. A significant share of that inertia lives in IT-led AI initiatives. The technical team owns the initiative. It has no commercial mandate to push through internal resistance. Business unit champions have both the decision-making authority and the incentive to remove blockers. Technology teams operate as infrastructure and compliance partners.
4. Build a cross-functional AI governance pod with real authority
Create a small, permanent team with decision-making authority across the functions that typically slow AI deployment: compliance, data governance, legal, and technology. This team doesn’t approve everything. It clears specific blockers that stall iterative development.
When DashDevs helped Dozens launch a licensed bank in 9 months, the governance architecture was designed from the start to support rapid iteration. Compliance was a structural input to each sprint.
5. Audit your approval chain against the regulation itself
Take your three slowest AI approval processes. Trace each step to the specific regulatory requirement it addresses. For each step, ask whether the requirement is in the regulation or in an internal interpretation of the regulation. Both are legitimate starting points, but only one is a compliance requirement the other side of an audit will actually look for.
Many of the approval chain steps that slow AI deployment in banks are interpretive accretion. Those are candidates for elimination without increasing regulatory risk.
Pro tip: After 17+ years integrating vendors into bank and PSP stacks, I start every AI programme by writing the risk-tier table before the vendor shortlist. If you can’t name which use cases get the short track, every model will wait in the long one.
What Good AI Governance Looks Like in Practice
The data from DBS, the CCAF 2026 report, and DashDevs’ own client work all point to the same governance model. It rests on three principles.
Risk proportionality. Not every AI use case carries the same risk. A low-risk internal analytics model should not require the same governance overhead as an automated credit decision system. The distinction matters more as AI volume scales.
Architecture first. Digital transformation services that succeed at embedding AI don’t add governance as a layer after the model is built. They design governance into the data architecture, the model lifecycle management system, and the deployment pipeline from the start.
Business ownership. The organizations where AI reaches production fastest are the ones where a business unit holds accountability for the outcome. That ownership drives the urgency to resolve governance blockers rather than wait for them to resolve themselves.
DashDevs’ AI-powered compliance platform for asset managers is a direct example of this approach: compliance as a designed capability.
Final Thoughts
Corporate bureaucracy in financial services is not going away. The regulatory environment that created it is not going away either. The question is whether the corporate bureaucracy your organization runs today was built for the pace that AI deployment requires.
The CCAF 2026 data shows that 81% of financial services firms are in the game. The meaningful gap is between the 6% of traditional FIs that have reached the transforming stage and the 19% of fintechs that have. That gap is organizational. It is closeable. And it is about building better governance.
If you need a partner to redesign that layer, start with fintech consulting or fintech software development. The EU DORA guide is the companion read when the bottleneck is operational resilience rather than model risk.
Share article
