


How to Write a Software Requirements Specification for Your Mobile App

September 5, 2026
- A well-written SRS is the document that aligns your dev team, prevents scope creep, and protects your mobile app budget before development begins.
- Requirements errors account for over 50% of budget overruns in software development.
- Mobile apps need SRS sections that most generic templates miss: device permissions, offline behavior, OS version ranges, and app store compliance rules.
- Functional specs define what the app must do; non-functional specs (performance, security, scalability) define how well it must execute.
Your dev team is lined up. You’ve got a product idea, some rough wireframes, and a budget. But you’re probably missing the one document that actually tells your developers what to build and, just as importantly, what to leave out.
That document is the software requirements specification (SRS), also called an SRS specification in some teams. Skipping it is one of the most reliable ways to run a mobile app project into the ground.
This guide is for product owners and startup founders who need a clear, structured mobile app requirements document before briefing a development team. We’ll walk through what a complete document includes, how to write each section, and what a real mobile SRS looks like in practice.
What Is an SRS?
An SRS is a formal document that defines what a software system must do. It covers required behavior and the constraints it operates within. It serves as the agreement between the people requesting the product and the team building it.
The term is sometimes written as software requirement specification. Both forms refer to the same document type, standardized under ISO/IEC/IEEE 29148.
For mobile apps specifically, the SRS does three things at once:
- It captures what the app must do (functional requirements)
- It describes how the app must perform (performance and security requirements)
- It sets the boundaries for scope, timeline, and the test strategy
Without it, development teams fill in the gaps themselves. Every gap they fill is a decision you didn’t make. That usually costs more to undo than to define upfront.
Large-scale software projects run an average of 45% over budget and 7% over schedule while delivering 56% less value than predicted. Unclear objectives and shifting scope/requirements account for over 50% of total cost overruns.
Why Generic SRS Templates Don’t Work for Mobile Apps
Most SRS templates are designed for enterprise web systems. A generic SRS template handles system architecture well. It rarely addresses what actually breaks mobile app projects.
Here’s what a mobile-specific software requirements document must cover that generic templates consistently miss:
| Mobile-specific area | Why it matters |
|---|---|
| Device permissions (camera, location, biometrics) | App stores reject apps with undeclared permissions at review |
| Offline behavior and data sync logic | Users lose connectivity; the app must handle this gracefully |
| Push notification architecture | Requires separate backend infrastructure and OS-level registration |
| App store submission requirements | Apple and Google have distinct rules that directly affect features |
| OS version and screen size ranges | Affects UI components, QA scope, and compatibility testing |
| Battery and background process limits | Unconstrained background tasks cause poor reviews and store flags |
If your SRS doesn’t address these areas, your team is guessing. Changing requirements mid-development can increase costs by up to 50%. That’s the average.
Functional vs. Non-Functional Requirements: What’s the Difference?
Understanding this distinction is essential before you write a single requirement.
Functional Requirements
They define specific actions the app must perform. Each one should be testable on its own.
The most reliable format: “The app shall [action] when [condition] so that [outcome].”
For a mobile banking app, a software requirements specification example looks like this:
- “The app shall send a push notification when a new transaction posts to the account so that the user is alerted without opening the app.”
- “The app shall cache the last 30 transactions for offline access so that users can review recent activity without a connection.”
Vague language like “the app should be fast” or “users should have a good experience” is not a functional requirement. It can’t be tested or accepted by a QA team.
Group them by feature area: authentication, onboarding, core transactions, notifications, and account settings.
Non-Functional Requirements
They define how well the system must perform. This is where most non-technical founders underspecify. It’s also where developers make the most consequential assumptions.
| Category | Mobile app example |
|---|---|
| Performance | App launch time under 2 seconds on mid-range Android |
| Availability | Backend API uptime of 99.5% or higher |
| Security | All data encrypted in transit (TLS 1.2+) and at rest (AES-256) |
| Usability | Primary actions reachable within 3 taps from the home screen |
| Compatibility | Full support for iOS 16+ and Android 12+ at launch |
| Scalability | The system handles 10,000 concurrent users without degradation |
The first category describes what a feature does. The second defines what acceptable performance looks like. You need both in writing before development begins.
For more on the role of a business analyst in a product launch and how they shape requirements documentation, see our dedicated article.
Why a Software Requirements Document Matters
An SRS is not an administrative hurdle. It’s the document that makes every downstream decision faster and cheaper.
Here’s what it protects you from in practice:
| Risk | What an SRS prevents |
|---|---|
| Scope creep | Undocumented assumptions become “features” mid-build, extending timelines and budgets |
| Rework cost | Defects caught during requirements cost a fraction of defects found in production |
| Misaligned QA | Without a requirements baseline, testers don’t have criteria to test against |
| App store rejection | Apple and Google review against specific rules; if those aren’t in your SRS, your team won’t build for them |
McKinsey and the University of Oxford studied 5,400+ IT projects and found an average 45% budget overrun. Poor requirements are the most common root cause. Understanding how much it costs to build an app starts with understanding how much an incomplete SRS costs you first.
The main challenge with most projects is that the plan was built on assumptions no one wrote down.
How to Write a Software Requirement Specification: 7 Steps
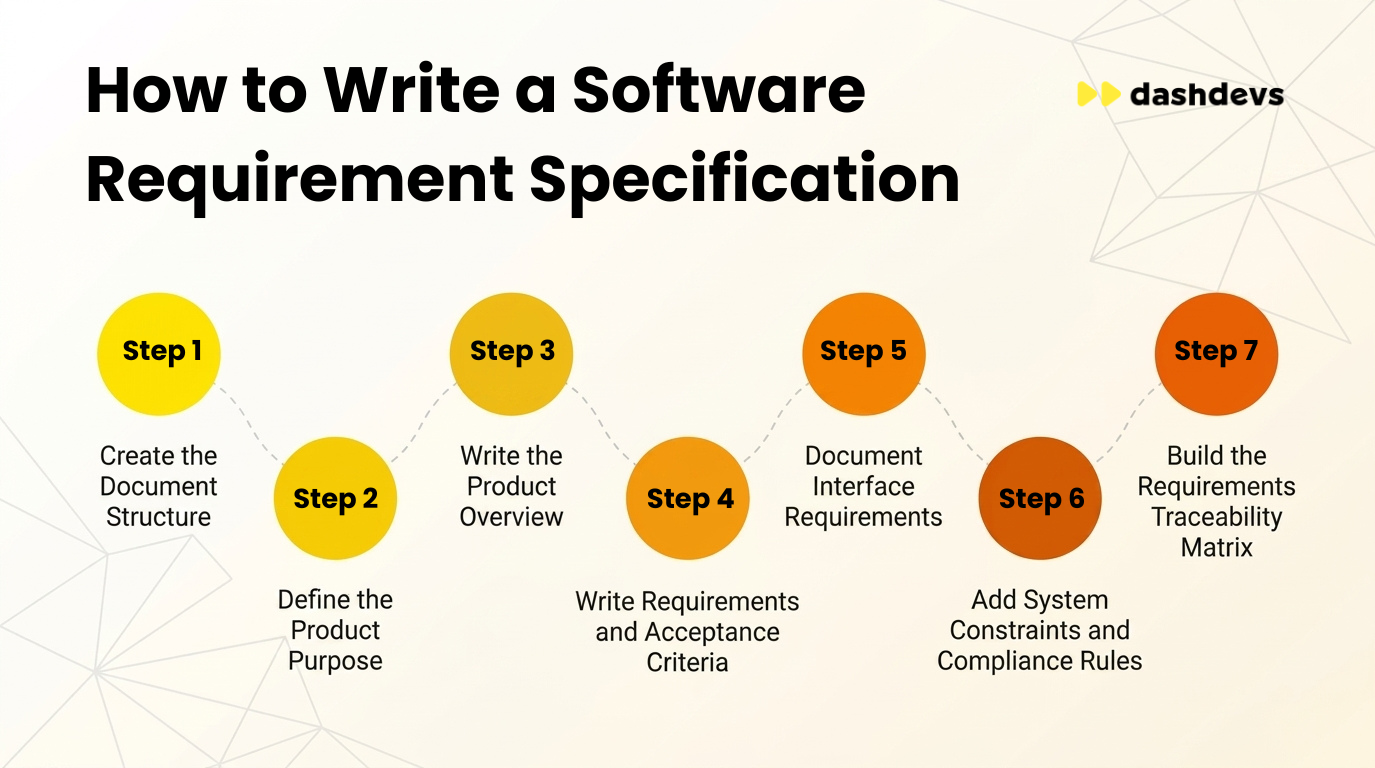
This is the requirements gathering process DashDevs uses with mobile product teams during the software product discovery phase.
Step 1: Create the Document Structure
Before writing any requirements, establish a clear outline. A well-organized structure improves readability for developers, QA engineers, and stakeholders reviewing the document before sign-off.
Standard sections for a mobile SRS:
- Introduction (purpose, scope, audience, definitions)
- Product overview (user types, system context, assumptions)
- Functional specs (by feature area, testable format)
- Performance and security specs (non-functional)
- Interface requirements (UI patterns, hardware sensors, third-party APIs)
- System constraints and compliance (app store rules, GDPR, PCI DSS where applicable)
- Traceability matrix (req ID, source, test case, status)
Use consistent section numbering (for example, 2.1, 2.2), so the dev team and QA can reference specific requirements without ambiguity.
Pro tip: Add a revision history table at the top. Requirements change. A versioned document shows who changed what and when. That matters during sprint reviews and scope disputes. Most software requirements specification template resources online provide this as an optional field. Make it mandatory for your team.
Once the SRS is signed off, it feeds directly into the statement of work in software development. The SOW scope is only as precise as the SRS behind it.
Step 2: Define the Product Purpose
This is where you answer: what problem does this app solve, for whom, and why now?
Write one sentence that captures the app’s core value.
For example: “An app that lets SME owners pay contractors across 12 countries from one interface, no bank account required.”
Every requirement you write afterward gets tested against this sentence. If a proposed requirement doesn’t serve this purpose, it belongs in a future version. The MVP vs. prototype distinction matters here, as it determines what ships first.
Include:
- The main problem the app solves
- Who benefits from the solution and in what scenario
- What the business outcome looks like when the app succeeds
Step 3: Write the Product Overview
The overview places the app in context. Cover who uses it, what systems it connects to, and what assumptions the team is making going in.
For mobile apps, this section should explicitly name:
- Target platforms (iOS, Android, or cross-platform)
- Minimum supported OS versions
- Backend and API dependencies
- Third-party integrations (payment providers, analytics, authentication)
- Key user roles (end user, admin, partner, etc.)
This section is also where you document scope exclusions. Stating “Version 1.0 will not include in-app payments or multi-language support” is a requirements decision. It protects the team from scope creep.
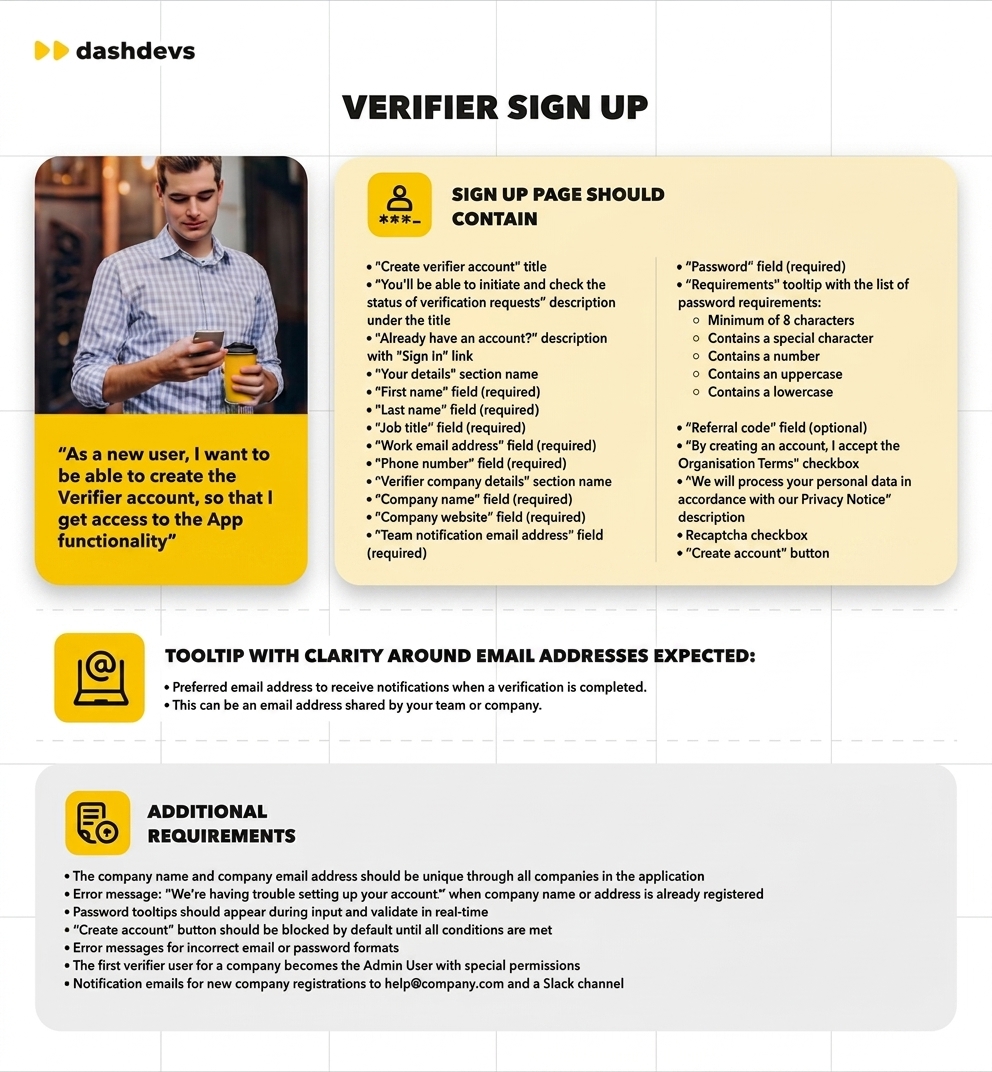
Here is an example overview structure from one of our project specs, a verifier sign-up flow:
Step 4: Write Requirements and Acceptance Criteria
This is the core of any good SRS. Write each requirement using testable language. Assign a specific measurable target to every performance or security spec.
Use the MoSCoW method (Must Have, Should Have, Could Have, Won’t Have) to prioritize. This makes sprint planning and scope negotiation much faster.
The most common omissions on the performance and security side:
- No defined minimum device spec for performance targets
- No specified encryption standard for data at rest
- No agreed uptime SLA for backend services
- No accessibility standard (WCAG 2.1 AA is the common baseline for consumer apps)
Each of these gaps becomes a debate during development, usually at the worst possible moment.
User stories and acceptance criteria belong here too. A user story describes the feature from the user’s perspective:
“As a user, I want to receive real-time notifications about my account activity so that I can detect unauthorized transactions immediately.”
The acceptance criteria define when that story is complete:
“The system must send a push notification within 60 seconds of a transaction posting. The notification must include the transaction amount, merchant name, and remaining balance.”

Without acceptance criteria, “done” means different things to the developer and the product owner. That gap is where QA disputes live. A good software requirements specification example always pairs each feature with at least one acceptance condition.
See also: how DashDevs approaches the discovery phase and how BAs structure requirements workshops to surface edge cases before sprint planning.
Step 5: Document Interface Requirements
This section covers every interface the app interacts with: user interfaces, hardware, and software systems.
For mobile apps, be specific:
- User interfaces: Reference wireframes and design files. Describe interaction patterns: swipe navigation, pull-to-refresh, biometric login, and bottom sheet dialogs.
- Hardware interfaces: Camera, GPS, Bluetooth, NFC, accelerometer, Face ID/Touch ID. State which features require which sensors and what happens when a device doesn’t support them.
- Software interfaces: List every API endpoint, authentication method, and third-party SDK. Include version requirements where relevant (for example, Stripe iOS SDK 23.x+, Firebase Messaging 10.x+).
Interface decisions affect your stack choices directly. Native camera access, offline-first sync, and biometric auth all constrain your technology options. See our breakdown of choosing the right technology stack for your mobile app and how those decisions connect.
The interface requirements section is where mobile projects most commonly hide integration risk. “We’ll connect to the payment API” is not a requirement. This is: “The app integrates with Stripe’s PaymentSheet SDK for iOS and Android. Supported methods: card, Apple Pay, and Google Pay. EU transactions require 3DS2 authentication.”
Step 6: Add System Constraints and Compliance Rules
Every mobile app project carries constraints the development team must work within. Document them before building, or discover them during the app store review.
Common constraints for mobile apps:
- Apple’s App Store Review Guidelines (privacy labels, permission declarations, in-app purchase rules)
- Google Play policies (content rating, permissions transparency, data safety section)
- GDPR data handling requirements (consent flows, data deletion, third-party data sharing disclosures)
- HIPAA compliance for health data (if applicable)
- PCI DSS scope for payment flows (cardholder data must never touch your servers if you use a compliant SDK)
Security requirements documented here carry through the entire secure software development life cycle. They define what your team must implement at each stage.
Fintech products require a longer compliance section than standard consumer apps. Fintech app development projects typically need a separate compliance annex that maps each regulatory rule to its technical implementation.
Step 7: Build the Requirements Traceability Matrix
This table links each requirement to its source, its test case, and its implementation status. It keeps your entire project aligned from specification through QA sign-off.
A basic matrix looks like this:
| Req ID | Requirement summary | Source | Test case | Status |
|---|---|---|---|---|
| FR-01 | The user registers via email with OTP verification | Product brief | TC-01, TC-02 | In dev |
| FR-02 | The app caches the last 30 transactions for offline access | UX research | TC-08 | Pending |
| NFR-01 | The app home screen loads in under 2 seconds on 4G | Performance spec | TC-15 | Passed |
| NFR-02 | All API calls use TLS 1.2 or higher | Security spec | TC-22 | Passed |
This becomes essential when your team grows or when you bring in a QA partner. When a stakeholder asks, “Why does the app not do X?” the answer should be in the matrix.
How DashDevs Writes Requirements for Mobile Products
Case Study: Centinel Insurance App
When DashDevs built the Centinel insurance app, the SRS work happened before the first sprint. That was a lean MVP, delivered in 4 months on a constrained budget. The team documented ML-driven risk-scoring logic, data processing workflows, and contract-generation rules as explicit, testable requirements. Each had acceptance criteria attached.
The result: 75% faster risk-assessment turnaround, 2x faster data processing, and 4x contract-generation efficiency. When requirements are vague, developers make conservative choices. Usually slower and safer ones.
Case Study: Tarabut Gateway
For Tarabut, the SRS covered interface requirements at a depth most startup founders don’t anticipate. This was MENA’s first regulated Open Banking platform. Integrating 24 Bahrain banks required precise API contract definitions and fallback behavior specs for every integration point. Security compliance requirements added another layer.
The platform reached a £25M valuation, integrated 8 banks in 6 months, and became MENA’s first regulated open banking platform. That delivery speed depends directly on requirements clarity upfront. Ambiguous specs in an open banking context don’t slow development. They stop it.
In open banking, the application requirements example that comes up most often is a missing error-handling spec for a bank API that returns an unexpected status code. If it’s not in the SRS, developers handle it however seems reasonable. That’s where the inconsistencies live.
Common Mistakes When Writing Mobile App Requirements
Writing functional requirements that can’t be tested. “The app should feel responsive” fails at QA. “The app home screen shall load within 1.5 seconds on a stable 4G connection” can be tested, accepted, or rejected.
Skipping app store requirements entirely. Apple and Google reject apps for undeclared permissions, missing privacy labels, and policy violations. If these aren’t in the SRS, your team won’t build for them.
Treating the SRS as a one-time document. Requirements change as you learn from user testing and stakeholder feedback. The SRS must be versioned and updated when scope changes. Otherwise, it becomes misleading rather than useful.
Omitting edge cases. What happens when the user loses connection mid-transaction? What does the app show on first launch with no cached data? These scenarios belong in the SRS. Without them, developers make their own choices, and those choices become bugs.
No sign-off process. A requirements document that hasn’t been formally reviewed and approved by key stakeholders is a draft. Get written approval from product, engineering, and QA leads before development begins.
This also matters when working with external teams. The best mobile app development outsourcing companies use the SRS to scope and price a project accurately. Without one, you’re comparing estimates that aren’t measuring the same thing.
What Comes After the SRS
The SRS is the beginning of execution. Once it is signed off, three things happen in sequence.
First, the development team can scope the build accurately. Second, the QA team has a baseline to test against. Third, every stakeholder has a shared reference when scope questions come up.
Projects with a solid SRS almost always cost less than ones without. Not because the scope is smaller, but because rework does not happen at production cost. A dedicated software development team from DashDevs works best when requirements are clear from day one.
Why You Need a Solid SRS to Avoid Costly Rework
A software requirements document is not bureaucracy. It’s how you protect your budget, your timeline, and your relationship with a development team.
Used correctly, this SRS document becomes the single source of truth your team references from kickoff through QA sign-off.
For mobile apps, the gaps in generic templates are the gaps that cause project failures. Undeclared device permissions, undefined offline behavior, missing app store compliance, and performance standards written so vaguely they can’t be tested.
The 7-step process above gives you the structure to write your own. If you want high-quality business analysis services, the product discovery service at DashDevs is built for exactly that.
Requirements engineering done right once saves you from doing everything else twice.
After 17+ years of shipping mobile and fintech products, the pattern is consistent: teams that lock testable requirements before sprint one rebuild less — and argue less about what “done” means.
Share article
