


Secure Software Development Lifecycle: 7 Phases for Fintech

October 9, 2026
- A secure software development lifecycle embeds security controls into every phase of delivery, from requirements through post-deployment operations, so vulnerabilities are caught before they reach production rather than after.
- Fintech teams under PCI DSS v4.0.1, DORA, and ISO 27001:2022 must treat the development lifecycle as an audit requirement: each framework names specific development-phase controls you must evidence at review time.
- The frameworks that matter most (PCI DSS v4.0.1, DORA, and ISO 27001:2022) each require phase-specific audit artifacts, not a single security report at the end of the sprint.
- AI-generated code and open-source dependencies have expanded the attack surface: SSDLC now requires SBOM generation, dependency pinning, and human review gates on AI-assisted commits.
- Your auditor isn’t asking whether you ran penetration tests. They are asking which phase of development you ran them in, what the findings were, and how you tracked remediation. That is the difference between a mature secure software development lifecycle and a security checkbox at the end of a sprint.
Your auditor isn’t asking whether you ran penetration tests. They are asking which phase of development you ran them in, what the findings were, and how you tracked remediation. That is the difference between a mature secure software development lifecycle and a security checkbox at the end of a sprint.
For CTOs and heads of engineering at fintechs and licensed financial institutions, this gap is consequential. PCI DSS v4.0.1, DORA, and ISO 27001:2022 each name specific development-phase controls. They expect evidence at every phase. If your SDLC wasn’t designed to produce that evidence, retrofitting it under audit pressure is expensive and slow.
This guide maps the full development lifecycle to the audit requirements of the three frameworks most relevant to regulated fintech, covers the two gaps that generic vendor guides consistently miss, and reflects what we actually see on the ground. Such as when we architected the MuchBetter e-wallet payment orchestration layer across SEPA and Faster Payments integrations, where designing for PCI DSS compliance from day one required treating security requirements as a strict upstream design input before a single line of backend Java was written.
What Is a Secure Software Development Lifecycle?
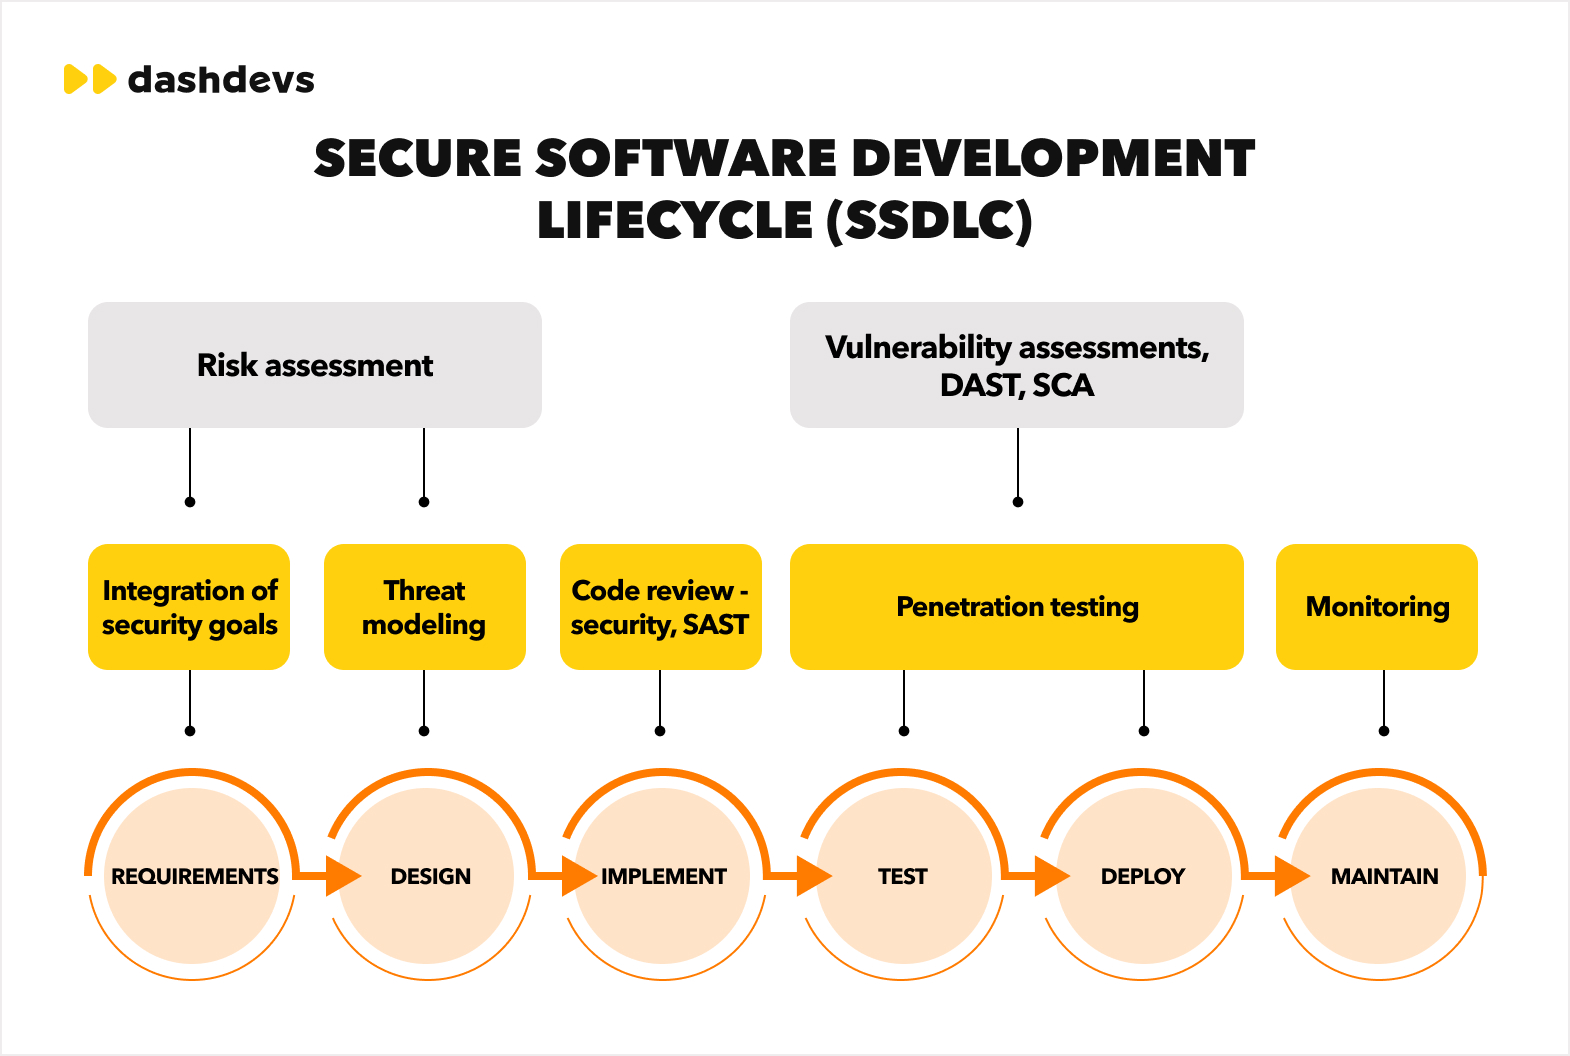
A secure software development lifecycle is a structured approach to software delivery in which security activities, controls, and review gates are built into every phase of development, from requirements gathering through post-deployment operations. Developing secure software at this level means security is a design input.
The core premise is simple: security issues caught in requirements cost a fraction of the same issue caught in production. The structural difference from a standard SDLC isn’t the addition of a security testing phase at the end. Security in software development only works when it is embedded from requirements. It is the integration of specific security activities throughout: threat modeling in design, SAST in implementation, DAST and penetration testing in verification, change-management controls in release, and continuous monitoring in operations.
Think of this phase as building a fortress. Every piece of code should strengthen the defenses, not create an entry point for potential threats.
SSDLC vs SDLC: Key Differences
The structural difference comes down to when security runs and who owns it, not whether a security team exists.
| Aspect | Standard SDLC | Secure SDLC |
|---|---|---|
| When security runs | Post-development testing phase | Every phase, from requirements onward |
| Cost of fixes | High — late discovery means rework | Lower — early discovery means targeted fixes |
| Threat modeling | Rarely, if ever | Phase 2: before any design work begins |
| Tooling | QA-focused | SAST, SCA, secrets scanning, DAST, pen testing, SBOM |
| Compliance evidence | Limited to test reports | Phase-specific artifacts at each stage |
| Developer accountability | Security is a security team problem | Every developer owns security in their code |
| AI/supply chain controls | Absent | SBOM, dependency pinning, AI code review gates |
The secure SDLC isn’t slower. Teams that front-load security reviews consistently spend less time on emergency patching and less time in audit remediation, which more than compensates for the upfront investment.
The 7 SSDLC Phases, Mapped to PCI DSS, DORA and ISO 27001
Regulated fintech teams need more than a phase or security in the SDLC phases list. They need to know which audit controls each phase produces evidence for in security SDLC phases. The table below maps each phase to the three frameworks most relevant to licensed fintechs operating in the EU, UK, and MENA.
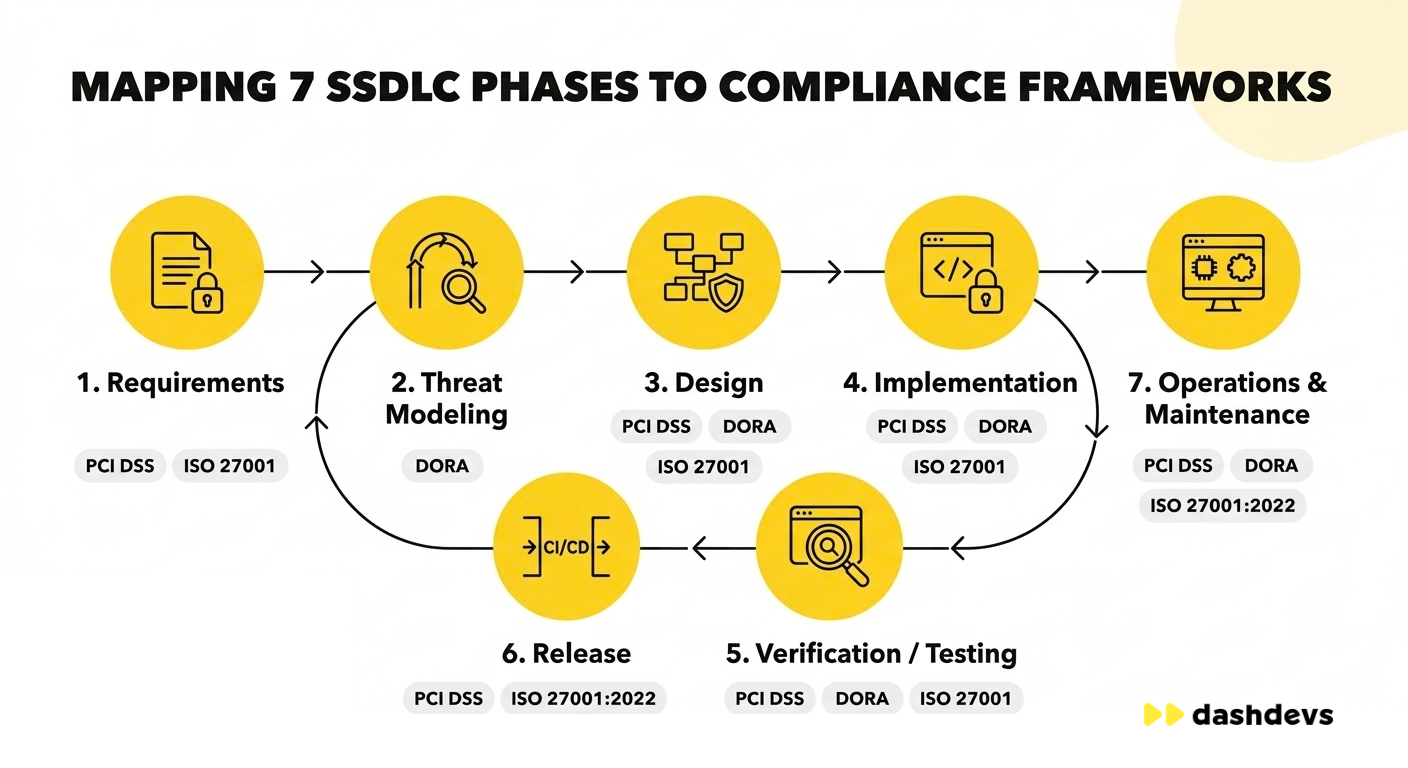
Regulation status as of October 2026: PCI DSS v4.0.1 is fully in force; DORA is fully in force for EU entities from January 2025; ISO 27001:2022 is the current version, and the transition from the 2013 edition is completed for most certified entities.
| Phase | Security activity | Key tooling | Audit evidence produced |
|---|---|---|---|
| 1. Requirements | Security requirements definition, data classification, regulatory scope mapping | Threat libraries, RACI templates | PCI DSS v4.0.1. Req. 6.2.1 (security requirements process); ISO 27001:2022 A.8.25 (secure dev policy) |
| 2. Threat modeling / Planning | Attack surface analysis, STRIDE or PASTA modeling, trust boundary definition | OWASP Threat Dragon, Microsoft Threat Modeling Tool | PCI DSS Req. 6.3.1 (vulnerability identification); DORA Art. 9 (ICT risk identification); ISO A.8.25 |
| 3. Design | Secure architecture review, zero-trust design, encryption decisions, secrets management strategy | Architecture review boards, design checklists | PCI DSS Req. 6.2.4 (bespoke software protection); ISO A.8.26 (secure coding); DORA Art. 9 |
| 4. Implementation | Secure coding standards, peer code review, SAST, SCA, secrets scanning, AI code review gates | SonarQube, Semgrep, Snyk, Gitleaks, GitHub Copilot review policies | PCI DSS Req. 6.2.4 (development techniques); ISO A.8.28 (secure coding); DORA Art. 9 |
| 5. Verification / Testing | DAST, API security testing, penetration testing, SBOM generation and validation | OWASP ZAP, Burp Suite, third-party pen testers, SBOM tools (Syft, CycloneDX) | PCI DSS Req. 6.3.2 (SBOMs); Req. 11.3.1 (vulnerability scan); Req. 11.4.1 (external pen test); DORA Art. 25 (testing); ISO A.8.29 |
| 6. Release | Change management controls, pre-production sign-off, security gate in CI/CD, build integrity verification | GitLab CI/CD, SLSA, artifact signing | PCI DSS Req. 6.5 (change management); DORA Art. 9 (ICT change management); ISO A.8.32 (change management) |
| 7. Operations & Maintenance | Continuous monitoring, patch management, vulnerability tracking, incident response, SBOM updates | SIEM, EDR, CVE feeds, MTTR dashboards | PCI DSS Req. 6.3.1 (patches); DORA Art. 10 (backups and recovery); ISO A.8.8 (vulnerability management) |
Security evidence isn’t produced by running tools. It is produced by running the right tools at the right phase and retaining the output in a form auditors can review.
Many teams get this backwards: they run SAST as a courtesy check after the code is written, then generate a report at audit time. That is SAST-washing.
SSDLC Frameworks: NIST SSDF, OWASP SAMM, Microsoft SDL and SLSA
The phases above describe what to do. Frameworks describe how to structure and mature your practice across the full application security lifecycle. Four are relevant for fintech.
NIST Secure Software Development Framework (SSDF)
The NIST SSDF (SP 800-218) organizes practices into four groups: Prepare the Organization (PO), Protect Software (PS), Produce Well-Secured Software (PW), and Respond to Vulnerabilities (RV). It is the most prescriptive of the four and maps cleanly to PCI DSS Req. 6 evidence requirements. If you are a US-based fintech or a MENA-licensed institution with a US parent, NIST SSDF is the most audit-legible framework available.
OWASP Software Assurance Maturity Model (SAMM)
OWASP SAMM scores your practice against five business functions: Governance, Design, Implementation, Verification, and Operations, each on a 1–3 maturity scale. It is the most useful framework for internal benchmarking and roadmap planning. Teams preparing for ISO 27001:2022 certification benefit from SAMM assessments because the maturity levels map naturally to the Annex A controls.
Microsoft Security Development Lifecycle (SDL)
Microsoft SDL is practitioner-oriented and prescriptive on tooling. Its strength is the implementation phase: specific requirements for SAST, fuzz testing, threat modeling processes, and incident response planning. Well-suited for teams building on Azure or integrating Microsoft identity and API tools.
Supply Chain Levels for Software Artifacts (SLSA)
SLSA is the framework most relevant to software supply chain security. The current stable version (v1.1) defines progressive security levels (SLSA 0–3) with strict requirements for build provenance. Level 1 requires provenance documentation so the build process is recorded. Level 2 adds a hosted build platform with signed provenance, so the output can be traced back to a verified source. Level 3 requires a hardened build environment with stronger isolation and tamper-resistance guarantees. For fintechs subject to DORA’s ICT supply chain requirements or PCI DSS Req. 6.3.2, SLSA Level 2 or above, provides defensible evidence that the build pipeline has not been tampered with.
Choosing a Framework by Regulatory Segment
The right framework depends on which regulatory obligation you are building evidence for first.
| Regulatory context | Recommended starting point |
|---|---|
| PCI DSS-scoped card program | NIST SSDF (maps directly to Req. 6) + SLSA for build integrity |
| EU EMI or PI preparing for DORA | OWASP SAMM assessment first, then NIST SSDF for evidence structure |
| ISO 27001:2022 certification track | OWASP SAMM (maps to Annex A 8.25–8.29) |
| US-regulated broker-dealer or RIA | NIST SSDF + Microsoft SDL for implementation tooling |
| Multi-jurisdiction (EU + UK + MENA) | OWASP SAMM for benchmarking, NIST SSDF for audit artifacts across all three |
If you are navigating multiple frameworks simultaneously, read our guide to fintech compliance regulations across the US, EU, UK and MENA for a jurisdiction-level comparison.
Two Gaps Most SSDLC Guides Miss
Generic vendor guides cover the seven phases adequately. Two areas are handled thinly across the top-ranking results. Both are active risk vectors for fintech teams in 2025–2026.
Software Supply Chain and AI-Generated Code Risk
The software supply chain is now a primary attack surface. Sonatype’s Q2 2025 Open Source Malware Index recorded 16,279 new malicious packages in a single quarter, with total open-source malware volume surging 188% year-on-year. The 2026 State of the Software Supply Chain report puts the full 2025 tally at 454,600+ new malicious packages across npm, PyPI, Maven, and NuGet, a 75% jump from the year before. For regulated fintechs, a compromised dependency isn’t only a security event; it is a PCI DSS Req. 6.3.1 and a DORA Art. 9 incident.
Three controls address this in software security:
- SBOM generation at every build: A software bill of materials enumerates every component and its version. For audit purposes under DORA and PCI DSS, it provides the evidence base for vulnerability tracking. Tools include Syft (SPDX/CycloneDX output) and Grype for automated CVE matching against the generated SBOM.
- Dependency pinning and SCA in CI/CD: Unpinned dependencies introduce supply chain risk at every build. SCA tools such as Snyk or Dependabot catch known vulnerabilities before they enter the main branch. This should run as a blocking gate.
- AI code review gates: Teams using GitHub Copilot, Cursor, or similar tools introduce a new risk category: AI-generated code that passes syntax checks but introduces logic vulnerabilities or insecure patterns. The control is a mandatory human review gate for all AI-assisted commits, combined with SAST scanning specifically tuned for AI-generated patterns, aligning with NIST SP 800-218A guidelines for Gen AI. See the discussion on AI code security on Fintech Garden, the DashDevs podcast, for a practitioner-level breakdown of where AI-generated code risks are currently concentrating.
Every dependency you don’t track is a vulnerability you haven’t yet discovered. SBOM generation isn’t optional for PCI DSS or DORA compliance. It is the foundation on which patch management evidence is built.
Development Lifecycle Metrics: Measuring What You Manage
Only one of the top-ranking secure SDLC guides covers metrics at all. For fintech CTOs, metrics matter for two reasons: internal planning and auditor scrutiny. An auditor asking for your vulnerability management process expects to see numbers.
Four metrics are worth tracking from the start:
- Mean time to remediate (MTTR) by severity: Track separately for critical, high, and medium findings. PCI DSS Req. 6.3.1 specifies patching timelines; MTTR data is the evidence.
- Share of builds blocked by security gates: This is the leading indicator of whether your security gates are functioning or bypassed. A figure below 5% may indicate gates are misconfigured or suppressed.
- Vulnerabilities escaped to production: Count of findings first discovered in production rather than in SAST, DAST or pen test. This is your software security failure rate. It should trend toward zero.
- Dependency age and known-CVE exposure: Average age of unpinned dependencies and count of components with active CVEs. Directly relevant to DORA Art. 9 ICT risk assessments.
Tracking these four metrics across quarterly reporting cycles produces the audit evidence trail that neither a test report nor a tooling screenshot alone provides.
If you want to understand how operational resilience controls under DORA translate to specific engineering requirements, that article covers Art. 9 and Art. 25 requirements in more depth.
Common Mistakes in Software Security Implementation
Teams in regulated fintech consistently repeat the same errors. Recognizing them early saves both engineering time and audit remediations.
- Running security as a phase. Adding a “security sprint” before release is a late-stage testing exercise with no upstream prevention. Findings at this stage routinely delay releases by weeks.
- Treating threat modeling as optional for internal tools. Internal admin panels and operations tooling process sensitive financial data. They sit within PCI DSS scope and under ISO 27001 controls. They need threat models.
- Suppressing security gate failures in CI/CD. Teams under delivery pressure suppress or override blocking security gates to hit a release date. Every override must be logged, reviewed, and approved by a named owner. In an audit, unapproved suppressions are findings.
- Skipping SBOM generation for legacy services. Teams generating SBOMs for new services but not legacy ones create a partial compliance picture that auditors will notice. SBOM coverage must be comprehensive.
- Conflating pen testing with DAST. DAST is automated; it finds known vulnerability classes quickly. Penetration testing is manual; it finds logic flaws and chained vulnerabilities that automated tools miss. PCI DSS Req. 11.3 requires both. Using only DAST and calling it a pen test is a common finding in PCI DSS assessments. Our penetration testing services team addresses exactly this gap.
DashDevs in Action
Describing a framework is straightforward. What changes under production conditions is where the complexity lives. Three projects illustrate specific secure SDLC decisions and their measurable outcomes.
Compliance-First Digital Banking Platform (Saudi Arabia)
The challenge for this Saudi banking client wasn’t building security controls; it was producing audit evidence in a form acceptable to SAMA’s Tanfeeth certification process. The platform required continuous customer screening, automated AML transaction evaluation, and isolated handling of high-risk cases, all with a full audit trail and decision traceability.
We built a multi-layered compliance architecture covering the AML screening pipeline, behavioral fraud engine, and unified case management environment. The secure development lifecycle was structured to produce regulator-grade artifacts at every secure SDLC phase: threat models during design, SAST reports during implementation, independent pen testing before each release, and real-time monitoring dashboards in operations.
The result: 100% SAMA Tanfeeth certification passed across all certification waves, a 50% reduction in AML alert false positives measured at post-go-live steady state, and a case investigation time cut from 48 to 24 hours through automated enrichment and workflow redesign. See the full details in our compliance-first digital banking platform case study.
Nexus Digital Banking Platform (Georgia)
Nexus is an all-in-one platform for building digital banks and embedding finance. The security challenge was a combination of legacy integration risk and transaction volume unpredictability: the platform needed to handle fluctuating loads while maintaining regulatory compliance and full data security across 50+ API endpoints.
We embedded OAuth 2.0, JWT authentication, and data encryption protocols across all backend services, implemented role-based access controls and automated compliance checks, and built an advanced API gateway with rate limiting and real-time monitoring as DAST-equivalent production observability.
The result: 100K+ transactions securely processed and 99.9% system uptime maintained in the first 7+ months of production. See the Nexus digital banking platform case study for full architecture details.
MuchBetter (UK, PCI DSS Payment Orchestration)
MuchBetter operates as an award-winning e-wallet serving 400K+ users across 180+ countries. The PCI DSS constraint was present from day one: every architecture decision needed to be compatible with the compliance scope, and the payment orchestration layer needed to connect multiple providers without expanding the cardholder data environment unnecessarily.
The secure development lifecycle implication was that security requirements were defined before any integration work began, each provider integration was threat-modeled individually, and the unified API interface was designed to isolate payment data flows from non-payment services. Dynamic security codes, device pairing, and biometric authentication were SSDLC design decisions. The result: a PCI DSS-compliant payment orchestration layer serving 400K+ users across 180+ countries with no cardholder data environment scope expansion across the full integration build. See our work with MuchBetter for the full scope.
If you are building a regulated payment product under PCI DSS constraints, the fintech architecture guide covers the structural decisions that determine your compliance perimeter.
What Auditors Actually Look For
Fintech teams often focus software security effort on tooling. Auditors focus on evidence. The two aren’t the same.
- For PCI DSS v4.0.1 Req. 6, auditors will request a documented secure development policy, evidence that threat modeling occurred before design was finalized, SAST scan reports for bespoke code with tracked findings, penetration test reports with remediation evidence, and change management records for production releases.
- For DORA Art. 9, the expectation is a documented ICT risk framework that covers the secure development lifecycle, with evidence that risks identified during development are tracked in the ICT risk register and addressed before production release.
- For ISO 27001:2022, the relevant Annex A controls (8.25–8.32) require a secure development policy, documented procedures for each phase, evidence of testing activities, and a formal change management process.
The consistent pattern: every framework wants a document, a process, and a dated artifact showing the process ran. If your secure development lifecycle generates no dated artifacts beyond a final test report, you have a documentation problem as much as a security problem.
For the specifics of working with an approved scanning vendor under PCI DSS, read our guide.
On the DORA side, our team discussed compliance as a design constraint on Fintech Garden — the specific engineering decisions that separate a DORA-ready architecture from one that will require expensive retrofitting.
The Security Cost of Waiting
Security that reaches production is exponentially more expensive than security caught in development. IBM’s Cost of a Data Breach 2026 report puts the average cost of a financial services breach at $4.99M, the second-highest of any industry. For a licensed fintech, that figure doesn’t include regulatory fines, license review risk, or reputational damage in a market where counterparty trust is the product.
The software security arithmetic is well-established. NIST and IBM Systems Sciences Institute research on defect-fix cost escalation consistently shows that the relative cost of fixing a vulnerability rises at each phase: roughly 1x in requirements, 3x in design, 5–10x in implementation, 10x in system testing, and 10–100x in production. The practical implication for fintech teams is that a finding blocked by SAST in a pull request costs a fraction of the same finding discovered during a PCI DSS penetration test and a fraction again of the same finding reaching production in a live cardholder environment.
The fintech teams that understand this treat software security as a commercial investment. The ones that treat it as a compliance burden consistently spend more on both. DashDevs has built the development lifecycle evidence trail for regulated products across PCI DSS, DORA, and ISO 27001, starting from requirements.
Fintech software development built on a mature development lifecycle produces fewer production incidents, shorter audit cycles, and faster time-to-market because security remediation isn’t blocking releases. Banking software development under DORA and PCI DSS has no path to a clean audit without it.
Share article
